Decrypt Compliance Explains SOC 2 Trust Principles and What Auditors Evaluate
CALIFORNIA, USA,- October 23, 2026- Decrypt Compliance, a specialized cybersecurity, privacy, and compliance auditing firm, is helping technology companies understand SOC 2 Trust Services Criteria (TSC), the controls auditors evaluate, and the evidence required during SOC 2 examinations.
The guide, titled “SOC 2 Trust Principles and What Auditors Evaluate,” explains the five SOC 2 Trust Services Criteria established by the American Institute of Certified Public Accountants (AICPA): Security, Availability, Processing Integrity, Confidentiality, and Privacy. It outlines their role in information security, operational reliability, data protection, and risk management.
Understanding SOC 2 Trust Services Criteria
Security is mandatory in every SOC 2 examination, while Availability, Processing Integrity, Confidentiality, and Privacy are included according to an organization's services, commitments, and examination scope.
The guide also covers the nine Common Criteria (CC1-CC9) associated with Security, addressing governance, communication, risk assessment, monitoring, control activities, access management, system operations, change management, and risk mitigation.
Examples illustrate how organizations can demonstrate their controls through access reviews, security awareness training, risk assessments, incident monitoring, change approvals, and vendor evaluations.
Evidence and Auditor Evaluation
The guide explains the importance of maintaining documentation and evidence demonstrating that controls are appropriately designed and operating effectively.
It covers Availability controls, including backups, capacity management, disaster recovery, and recovery testing. Processing Integrity focuses on accurate, complete, authorized, and timely data processing. The guide also explains how Confidentiality and Privacy address sensitive information protection and personal data management.
Written policies alone may not be sufficient. Depending on the examination scope, auditors may review system configurations, access records, monitoring logs, approvals, and other supporting evidence to evaluate control effectiveness.
Cybersecurity Risks and Audit Readiness
The guide references PwC's 2024 Global Digital Trust Insights research, which reported that the proportion of respondents whose most damaging data breach in the preceding three years cost at least $1 million rose from 27% in 2023 to 36% in 2024.
The resource is designed for startups, SaaS providers, fintech companies, small and medium-sized businesses, and cloud service organizations preparing for SOC 2 examinations.
The guide is educational and does not replace official AICPA criteria or an independent auditor's assessment.
About Decrypt Compliance
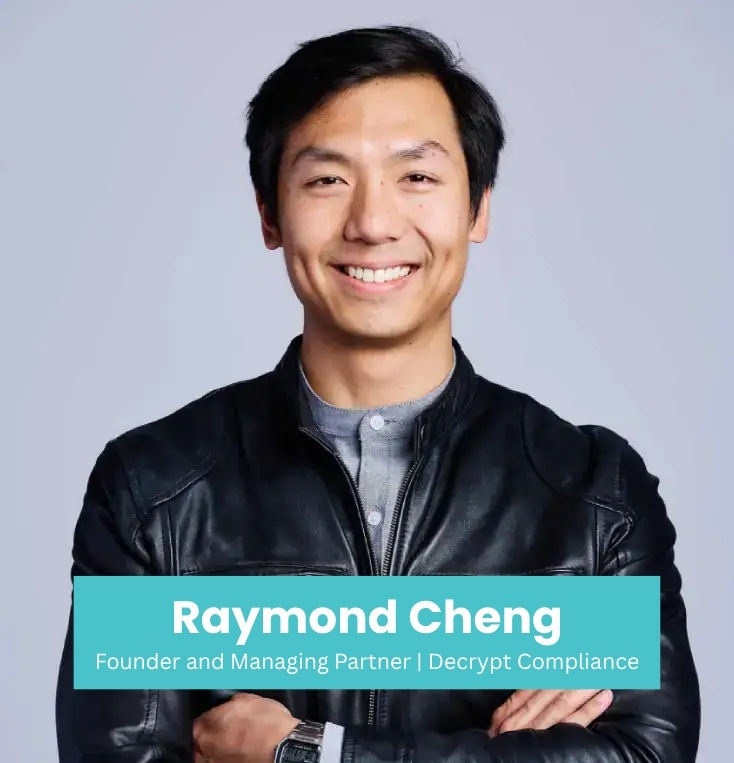
Decrypt Compliance is a Silicon Valley-based CPA firm specializing in cybersecurity and compliance audits. The firm provides SOC 2, ISO 27001, HITRUST, and privacy compliance services. It supports B2B SaaS and technology companies in meeting security requirements. Founded by Raymond Cheng, CPA, CITP, CISA, and CISSP, it combines technical and accounting expertise. In 2026, Raymond Cheng was named to Forbes’ Best-In-State CPAs list. Decrypt Compliance helps businesses strengthen customer trust and simplify compliance.
Media Contact:
Decrypt Compliance, Raymond Cheng
3031 Tisch Way, 100 Plaza West,
San Jose, CA 95128, United States
Email: info@decrypt.cpa
Website: https://decrypt.cpa/
View the Original Press Release on SP Tech Solutions.